Security research · home lab
Wir3less
A home-network security training dashboard for eJPT and OSCP study
A .NET dashboard built to practise the eJPT and OSCP curriculum against the author's own network: it discovers devices, watches local traffic, and drives a Kali Linux VM to run recon safely from one place.
The challenge
Learning practical security means running real tools, but doing that safely needs a controlled lab, a clear ethical scope, and somewhere to see the results without jumping between a dozen terminals.
The approach
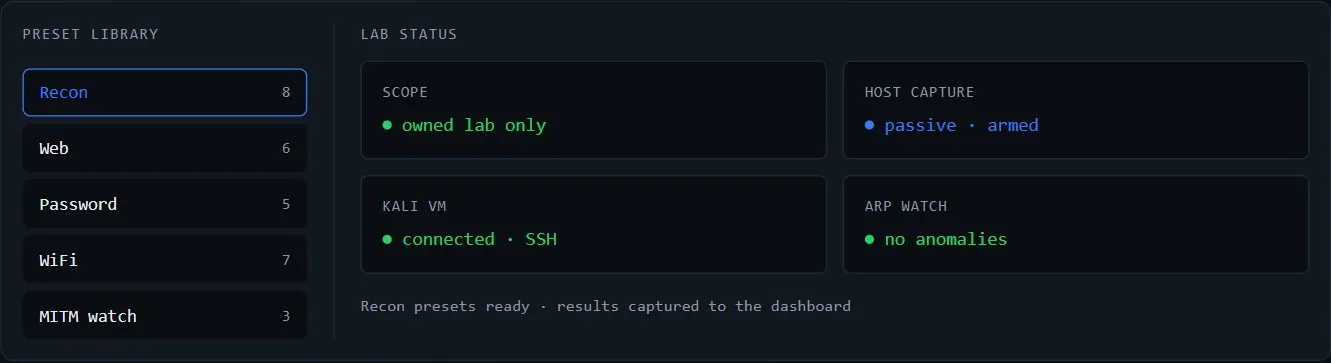
Native packet capture watches the Windows host's own traffic for things like ARP spoofing, while everything active is run on a Kali Linux VM orchestrated over SSH. The dashboard is a categorised library of presets, kept strictly to networks we own.
Features
- Device discovery: Reads the local network to list what's connected, as a starting point for everything else.
- Traffic watch: Passive packet capture flags suspicious patterns like ARP spoofing on the host's own traffic.
- Kali orchestration: Drives a Kali Linux VM over SSH, so recon and scanning run in a controlled lab, not on the Windows host.
- Preset library: A categorised set of saved workflows, so study sessions are repeatable and documented.
- Owned networks only: The whole project has a written ethical scope: it is only ever pointed at hardware and networks we control.
- Session log: Each lab session is recorded, so what was run, when and against which lab machine is easy to review.
Outcomes
- A repeatable home lab for studying for security qualifications
- Kept to a written scope: only our own hardware and networks
Built with
- Blazor
- .NET 10
- SharpPcap
- SSH.NET
- Kali Linux