Security research · defensive
Nullroute
A live network threat monitor that maps who's hitting your edge
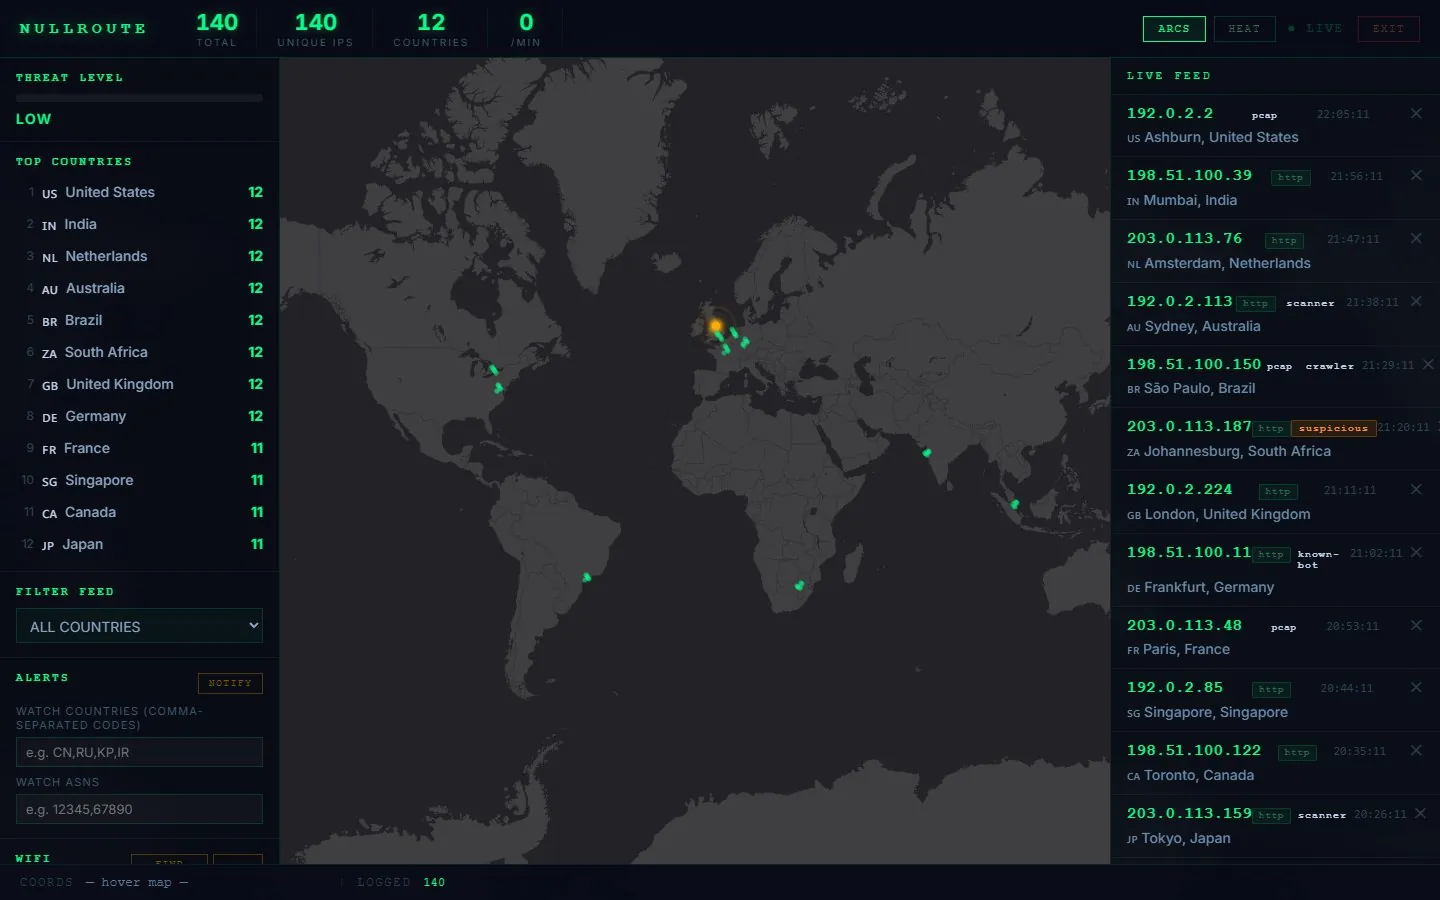
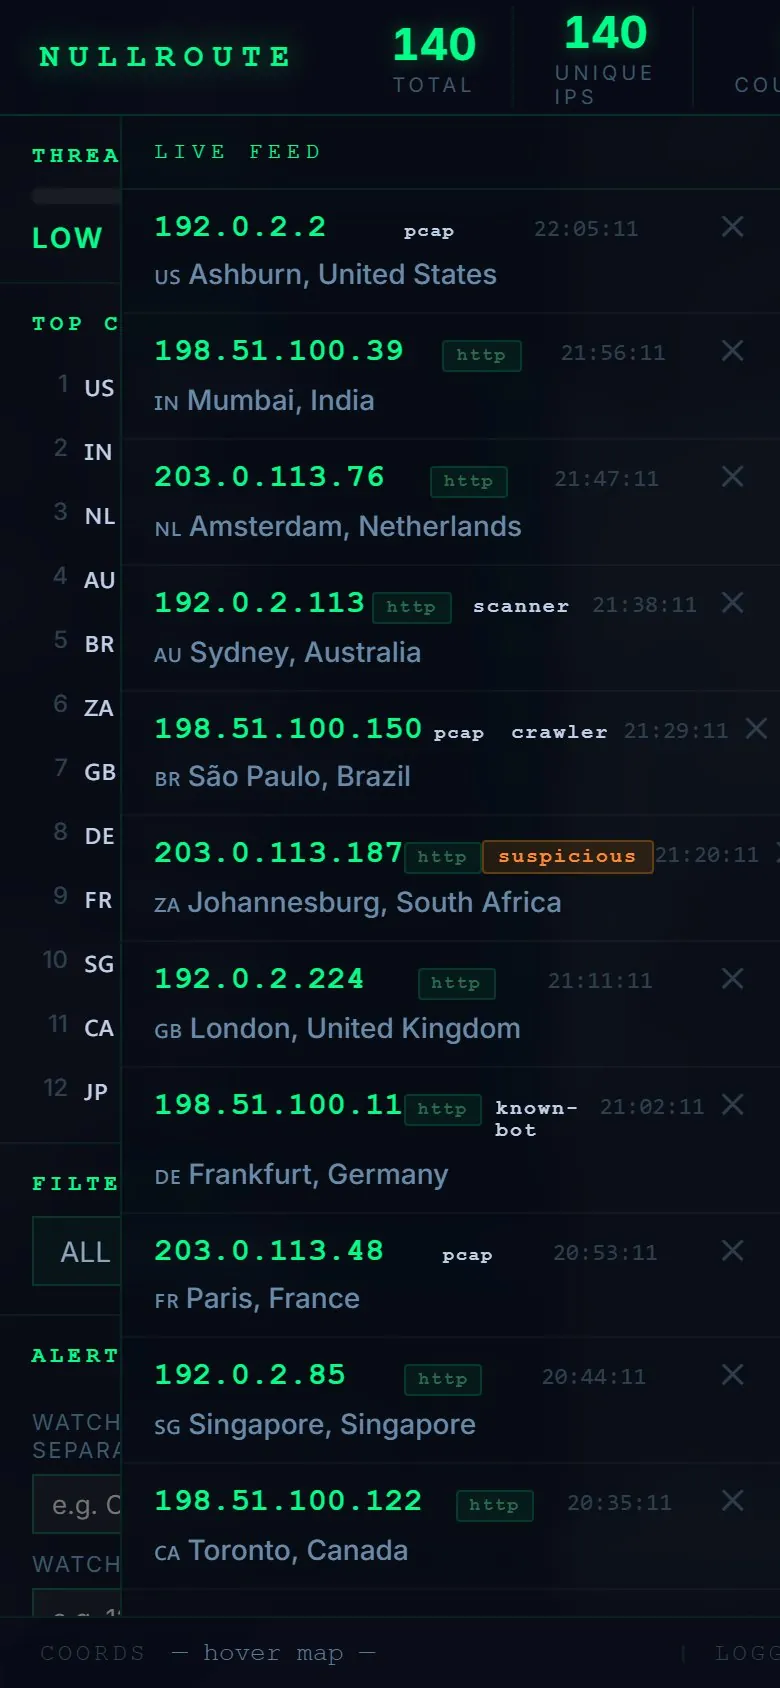
A defensive monitoring web app that captures traffic, records every IP that reaches the host, locates it on a map, and streams it to a live dashboard. Built and run only on our own network.
The challenge
You can't defend an edge you can't see. Raw packet logs are unreadable in real time, and a list of IP addresses tells you nothing about where traffic is really coming from.
The approach
Packet capture with SharpPcap feeds a pipeline that records each IP hit, looks it up against a MaxMind geolocation database, and pushes it to the browser over a SignalR hub. The API is hardened by default with auth and security-header middleware, and the whole thing is documented with Swagger.
Features
- Live IP hit feed: Every IP that reaches the host is captured and streamed to the dashboard in real time over SignalR.
- Geolocation: Each hit is placed on the map with a MaxMind GeoIP lookup, so traffic patterns are visible at a glance.
- LAN and WiFi view: Separate views track devices on the local network and the WiFi networks seen around it.
- Hardened by default: Auth, IP-capture and security-header middleware sit in front of every request, with the data model managed through EF Core migrations.
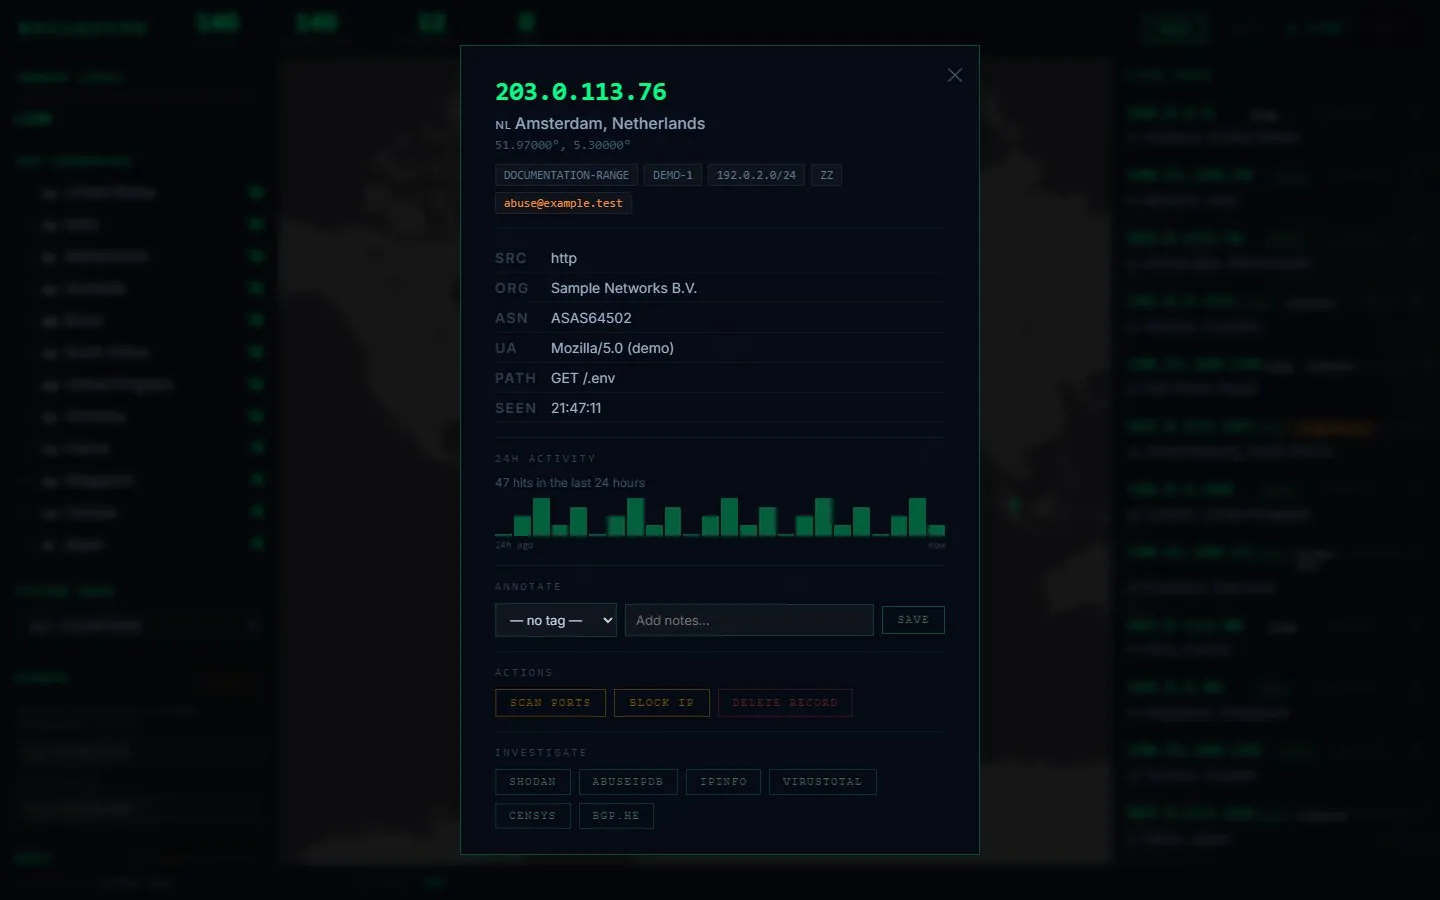
- Investigate any IP: Open a hit for its location, network, 24-hour activity, a WHOIS summary and links out to reputation services.
- Tag, annotate and block: Label an address, add notes or block it, and set alerts for the countries or networks you care about.
Outcomes
- Every request that reaches the host is located and shown on the map as it happens
- Runs only on our own network and hardware, as a way to learn what real internet background noise looks like
- Screenshots use addresses from the reserved documentation ranges, not real visitors
Built with
- ASP.NET Core
- EF Core
- SQL Server
- SharpPcap
- MaxMind GeoIP
- SignalR