Security research · tooling
MetroBoomin
An automated harness that runs security checks against a target you own
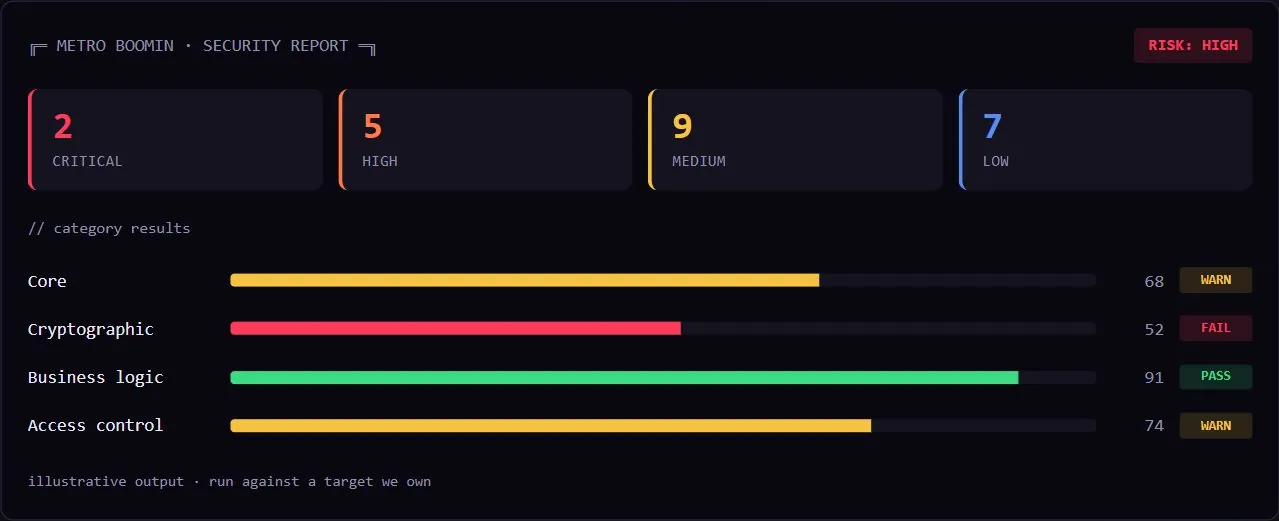
A .NET command-line harness that runs categorised security checks against a target application — like DotNetGoat — and writes up what it finds. Built to understand how automated testing tools work by building one.
The challenge
Automated scanners feel like magic until you've written one. Understanding how they categorise checks, drive them from a profile and report findings is the best way to read their output critically.
The approach
A console tool organised around attack profiles and distinct check categories — core, cryptographic and business-logic — with a report generator that collects the findings. Pointed only at deliberately vulnerable targets we run ourselves.
Features
- Profile-driven runs: Checks are grouped into profiles, so a run can be scoped to exactly what you want to test.
- Categorised checks: Separate core, cryptographic and business-logic suites, each a self-contained module.
- Findings report: A report generator collects everything a run turns up into one readable write-up.
- Pairs with DotNetGoat: Designed to be pointed at our own vulnerable-by-design target, never anyone else's system.
- Severity at a glance: Findings are graded by severity, so the report leads with what matters most.
- Repeatable runs: The same profile gives the same checks every time, which makes before-and-after comparisons meaningful.
Outcomes
- Runs only against DotNetGoat and other systems we own
- Turned a long manual checklist into one repeatable run with a written report
Built with
- C#
- .NET 8
- Console