Security research · learning target
DotNetGoat
A deliberately vulnerable shop, built to learn the OWASP Top 10 on
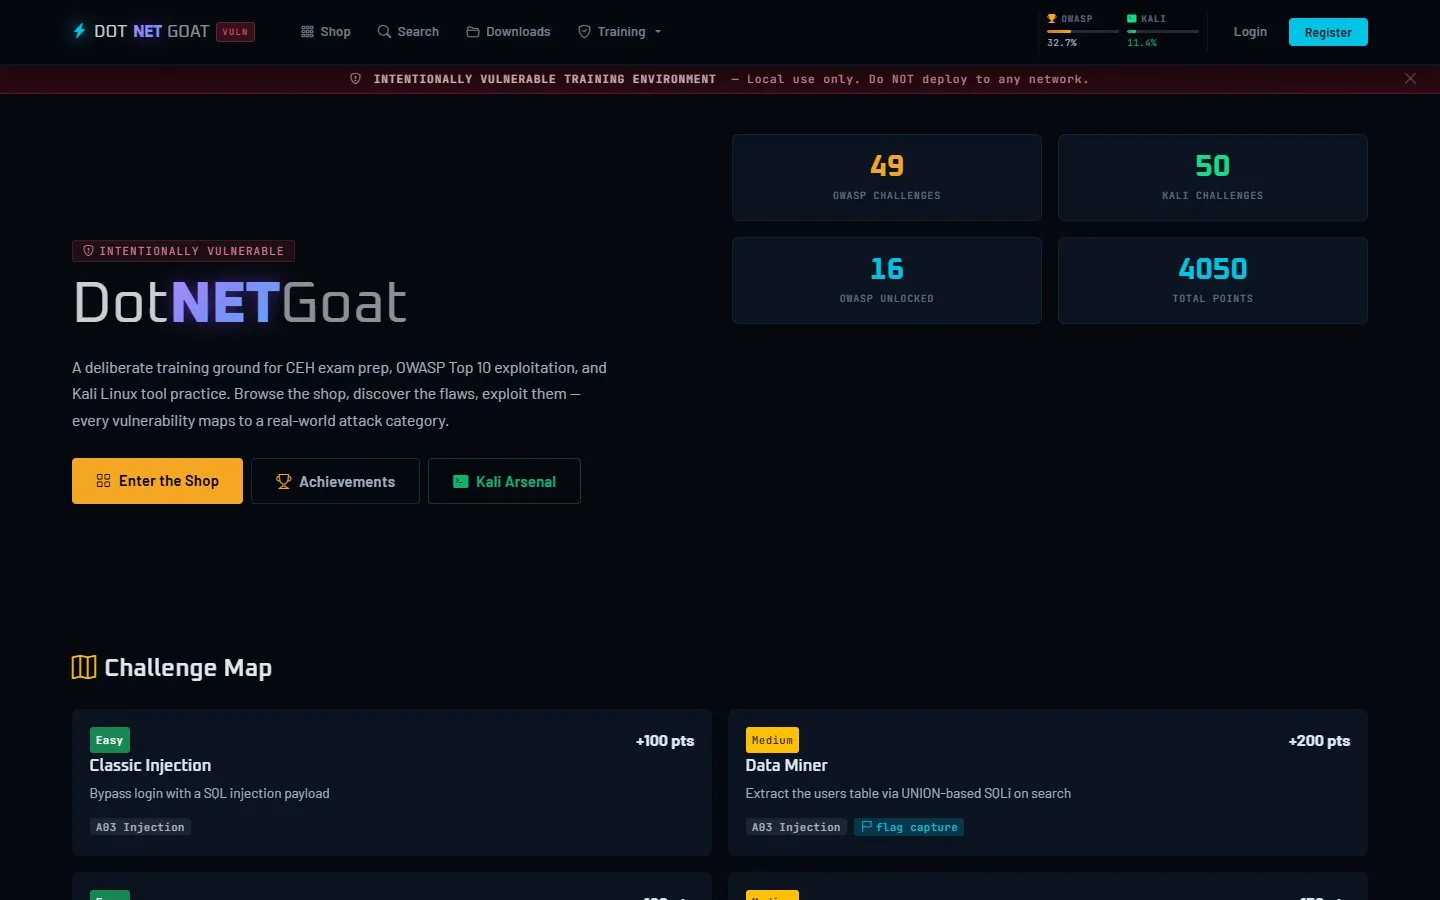
BreakPoint Boutique: an intentionally broken e-commerce app seeded with real, working vulnerabilities mapped to the OWASP Top 10, with a gamified achievement system that tracks what you've found. A safe target, run only on a local machine.
The challenge
You learn far more about a vulnerability by exploiting it and then fixing it than by reading about it, but you need a safe, legal target to do that against.
The approach
A full e-commerce app, inspired by OWASP Juice Shop, deliberately seeded with the OWASP Top 10. An achievement system tracks progress, and each flaw is paired with a secure-coding 'before and after' so the fix is as clear as the break. Carries a loud notice never to expose it to a real network.
Features
- OWASP Top 10, on purpose: Real, working vulnerabilities across the Top 10, each one a deliberate lesson rather than an accident.
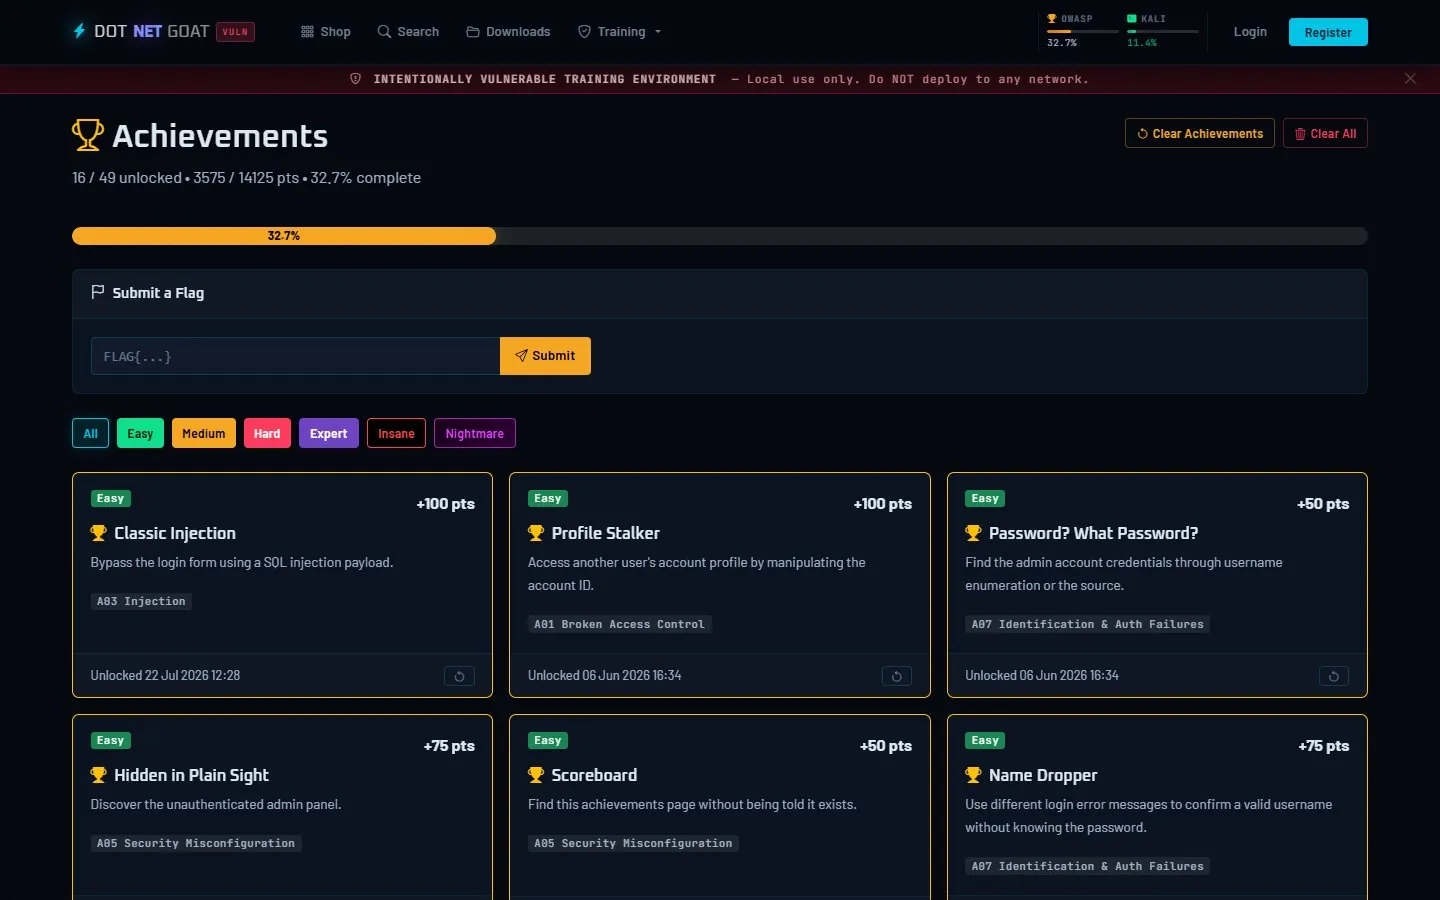
- Gamified progress: An achievement system tracks what you've discovered, which makes a dry checklist something you actually finish.
- Fix, not just find: Every flaw comes with a secure-coding before-and-after, so the point is defending the code, not just breaking it.
- Interview-ready: Built as something concrete to talk through when demonstrating secure-coding knowledge.
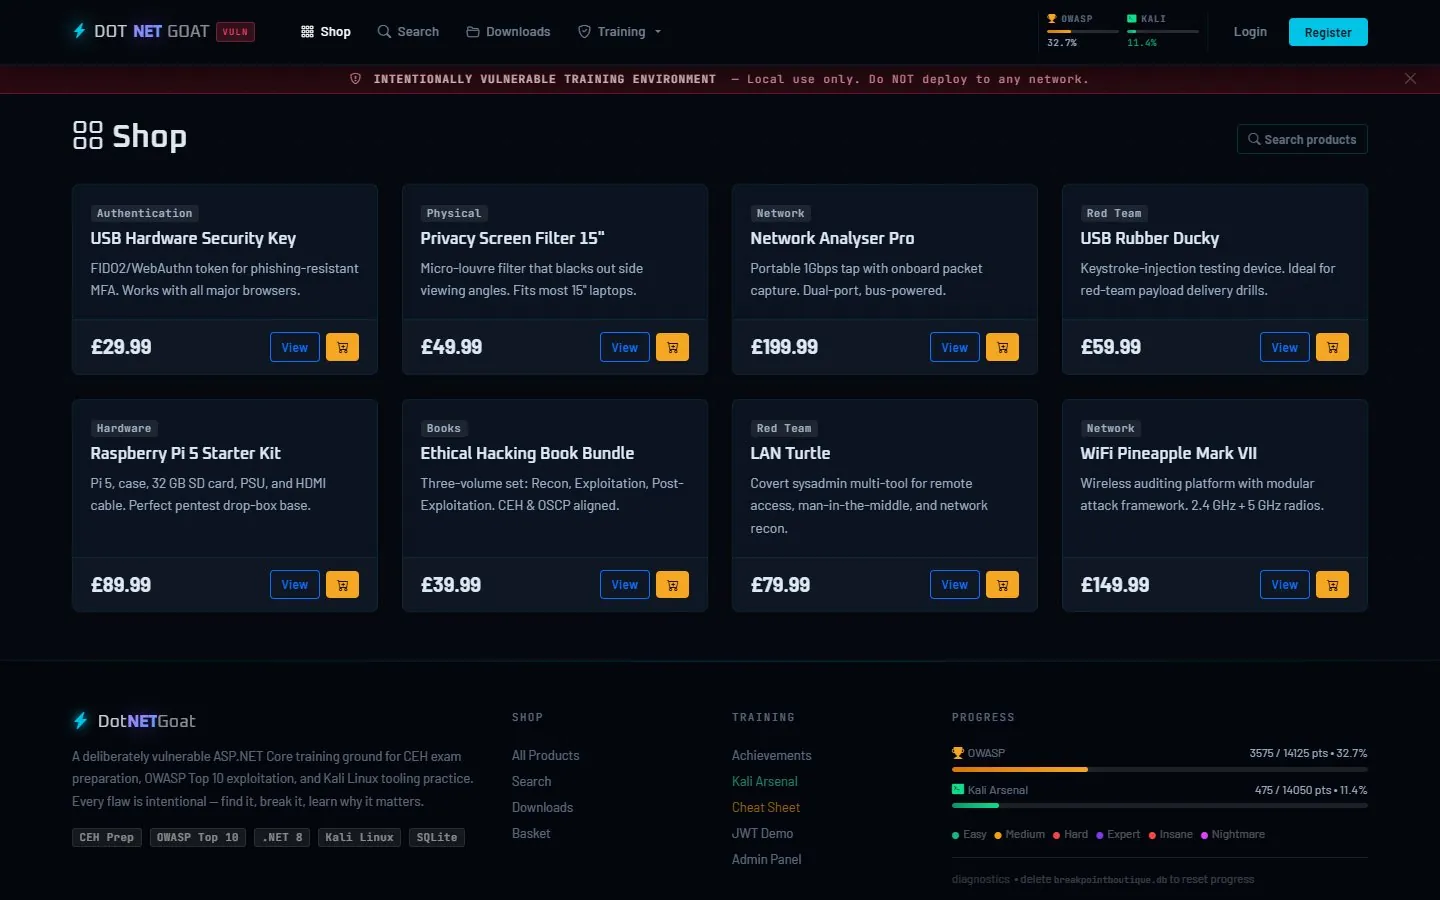
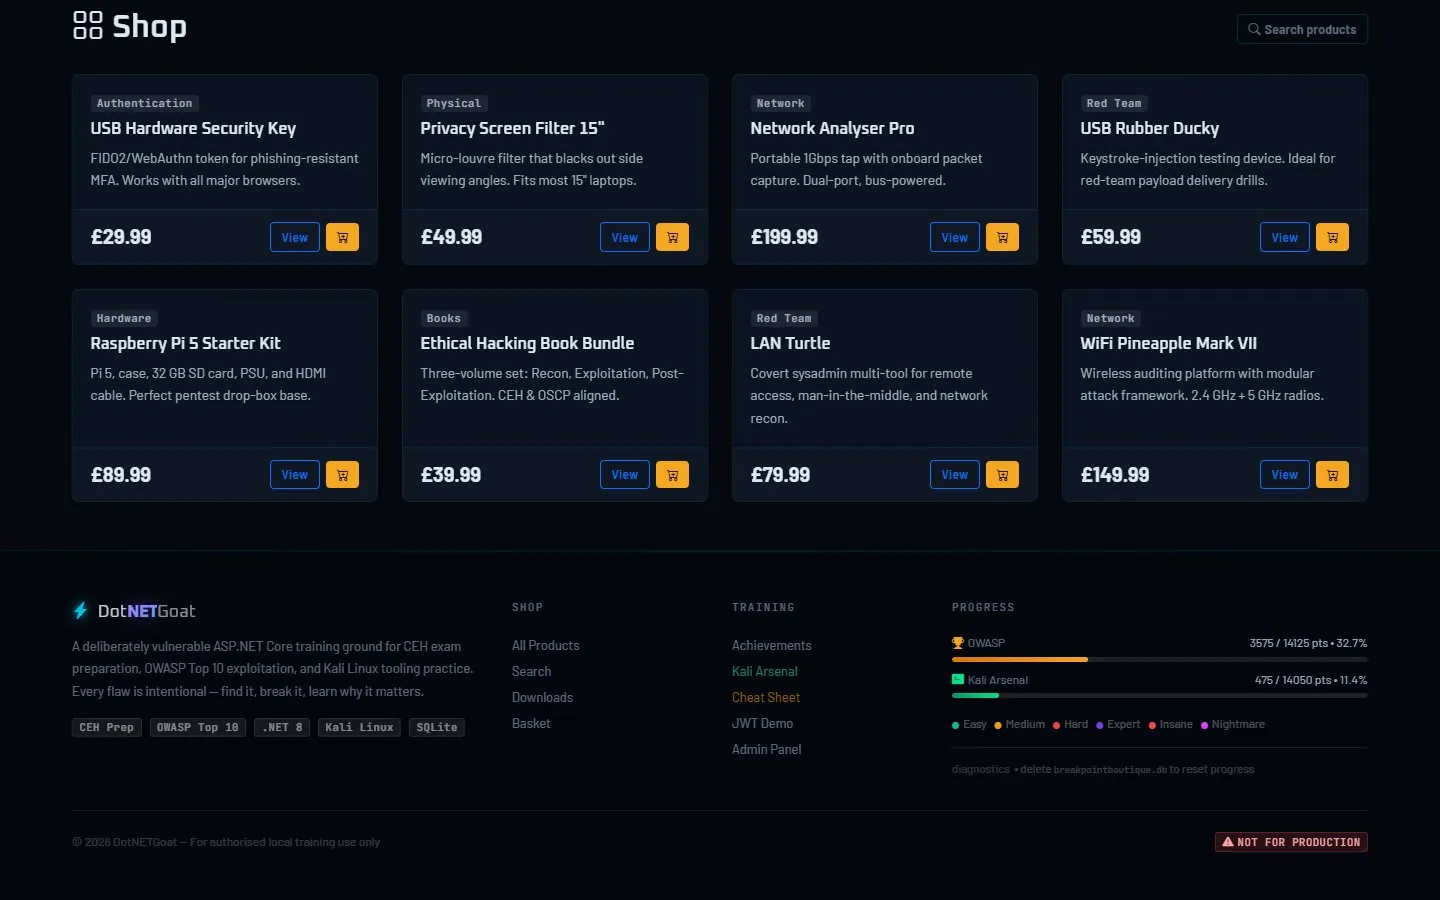
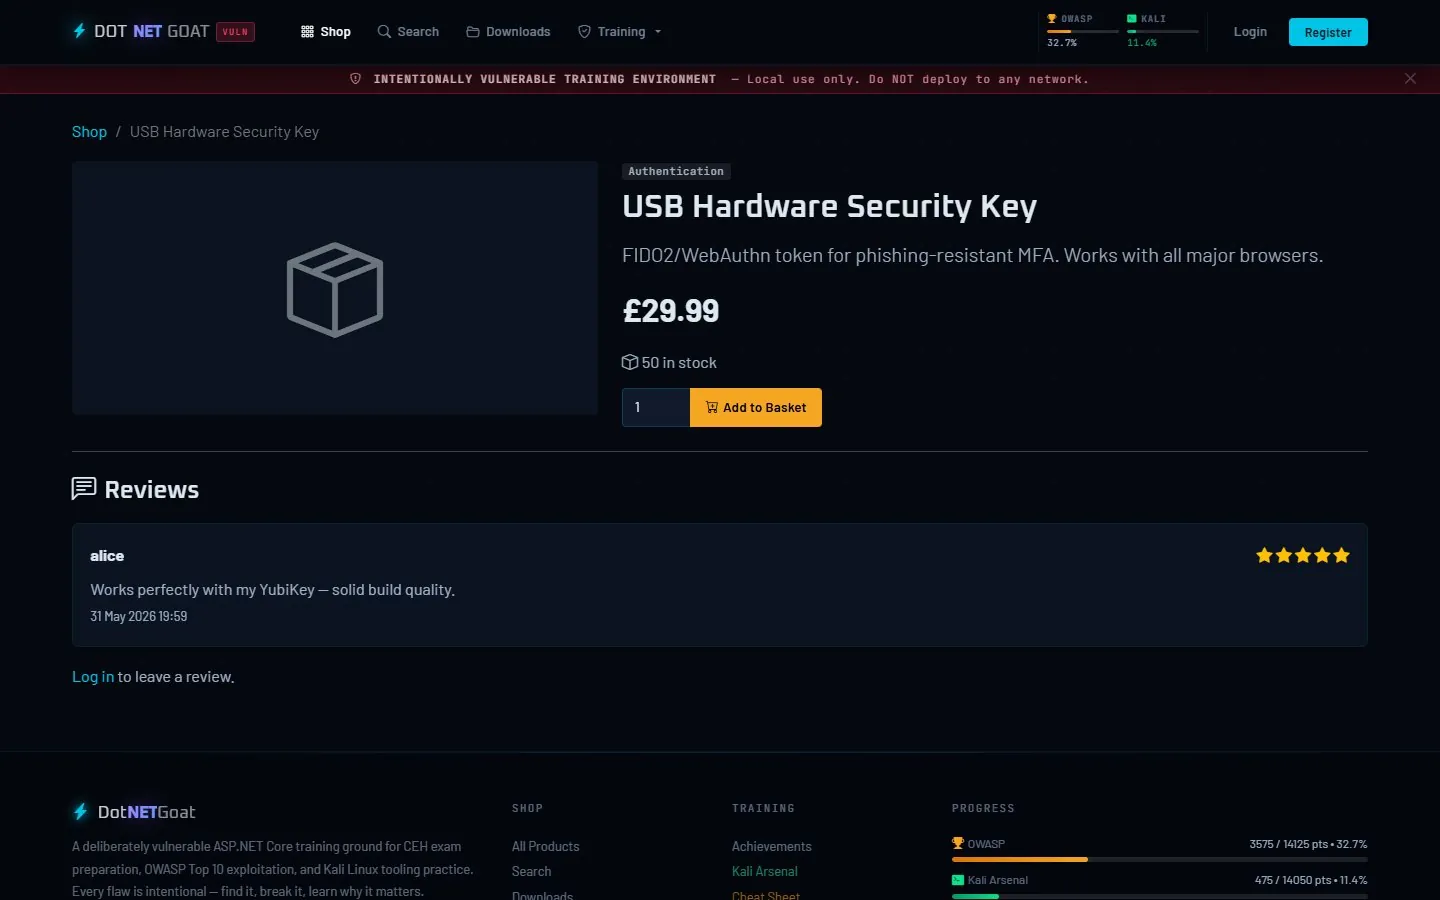
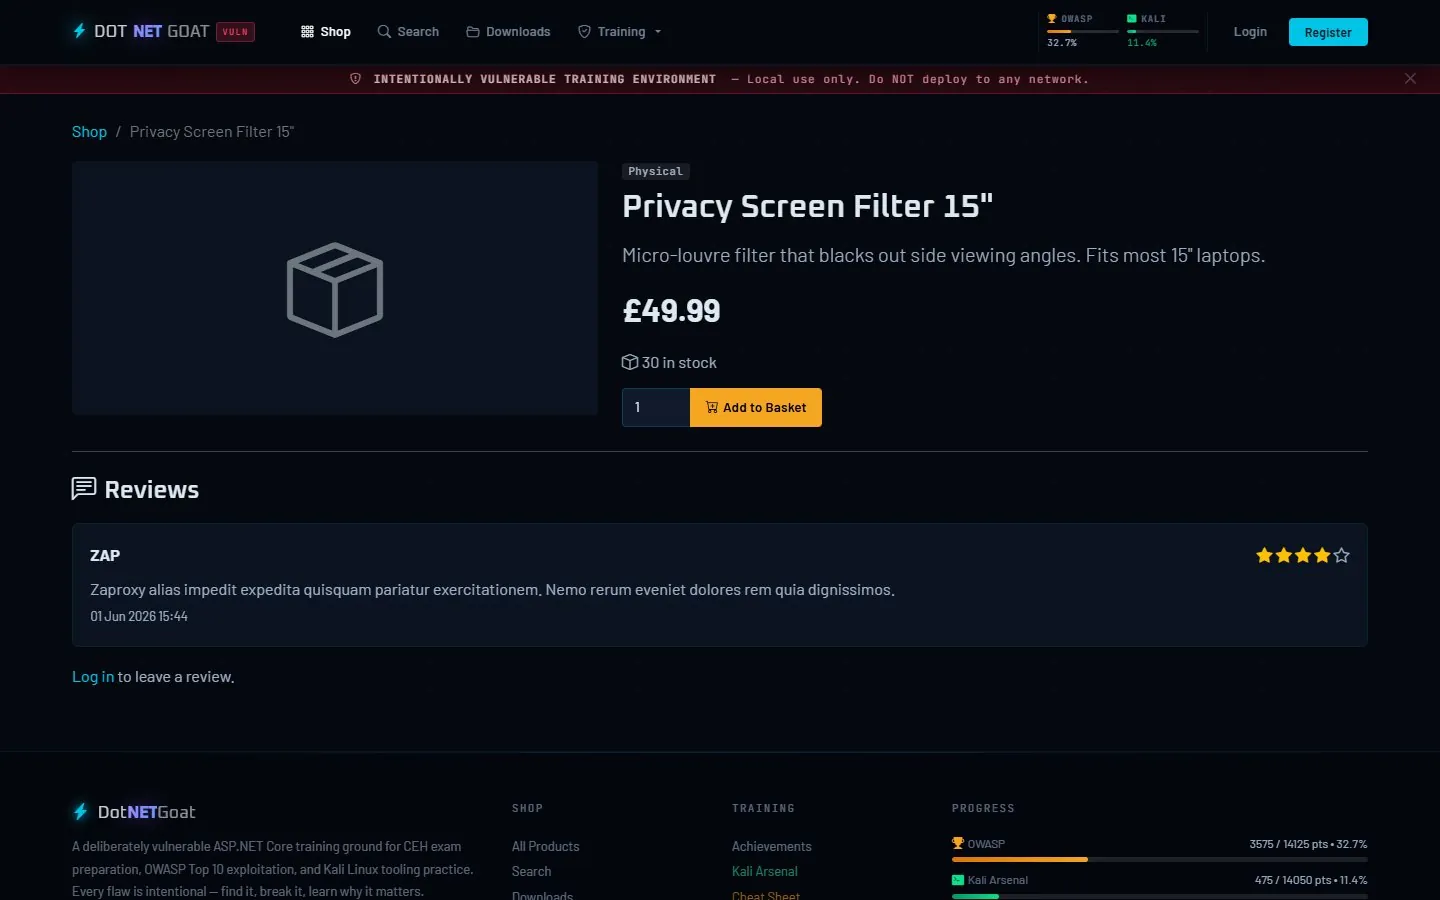
- A real shop to explore: BreakPoint Boutique has a catalogue, product pages, reviews, a basket and accounts, so the flaws sit in realistic features.
- Local only, clearly labelled: A banner on every page marks it as an intentionally vulnerable training environment for local use only.
Outcomes
- 49 OWASP challenges and 50 tool-practice challenges, each tracked on the achievements board
- Runs on localhost with a SQLite database, so it is quick to reset and never exposed
- Used alongside MetroBoomin as a safe target for our own testing tools
Built with
- ASP.NET Core
- .NET 8
- OWASP Top 10